Prompt injection in MCP: first win the tool call, then redirect the agent
A two-stage MCP prompt injection study wins tool calls with optimised metadata, then redirects agents through malicious tool returns. Both boundaries need policy.
Promptective journal
Articles, practical guides and product news for teams governing AI across browsers, desktops and agents.

Zenity Labs shows how an indirect prompt injection in a public Web-to-Lead form reached Salesforce Agentforce account data and Slack. The reported chains are patched.

Stop unauthorised workplace AI use with approved tools, clear data rules, scoped technical controls, expiring exceptions and a practical verification checklist.

Promptective now supports Amp.
Stories and analysis

A two-stage MCP prompt injection study wins tool calls with optimised metadata, then redirects agents through malicious tool returns. Both boundaries need policy.

A revised study shows how forged mailbox faults can steer email agents into unauthorised actions, and why verified state and action authorisation are separate checks.

A new preprint labels each input token with its origin and adds a learned attention bias, reporting near-zero prompt-injection attack success.

Straiker’s lab shows how indirect prompt injection in telemetry led an SRE agent to deploy a privileged Kubernetes workload, enabling ransomware effects.

Unit 42’s AWS AgentCore prompt injection research shows how shell access exposed an in-use credential, with lessons for tool scope and runtime isolation.

Exocija says DeepSeek V4.1 Flash found a race use-after-free in Samsung’s sgpu GPU driver. Here is what the claim shows about AI vulnerability discovery, and what remains unverified.

Research finds malicious LLM API routers rewriting agent tool calls and abusing credentials. Learn the findings, defence limits and checks for security teams.

Google reports a DUSTMAKER prompt injection attack targeting coding assistants. Learn how workspace instructions cross trust boundaries and what teams can check.

Explore multimodal prompt injection examples from a new preprint, and learn why attempted actions, tool calls and completed attacks need separate measures.

CVE-2026-82233 let SiYuan’s AI agent copy sensitive local files through MCP, showing why tool approvals need action-level policy.

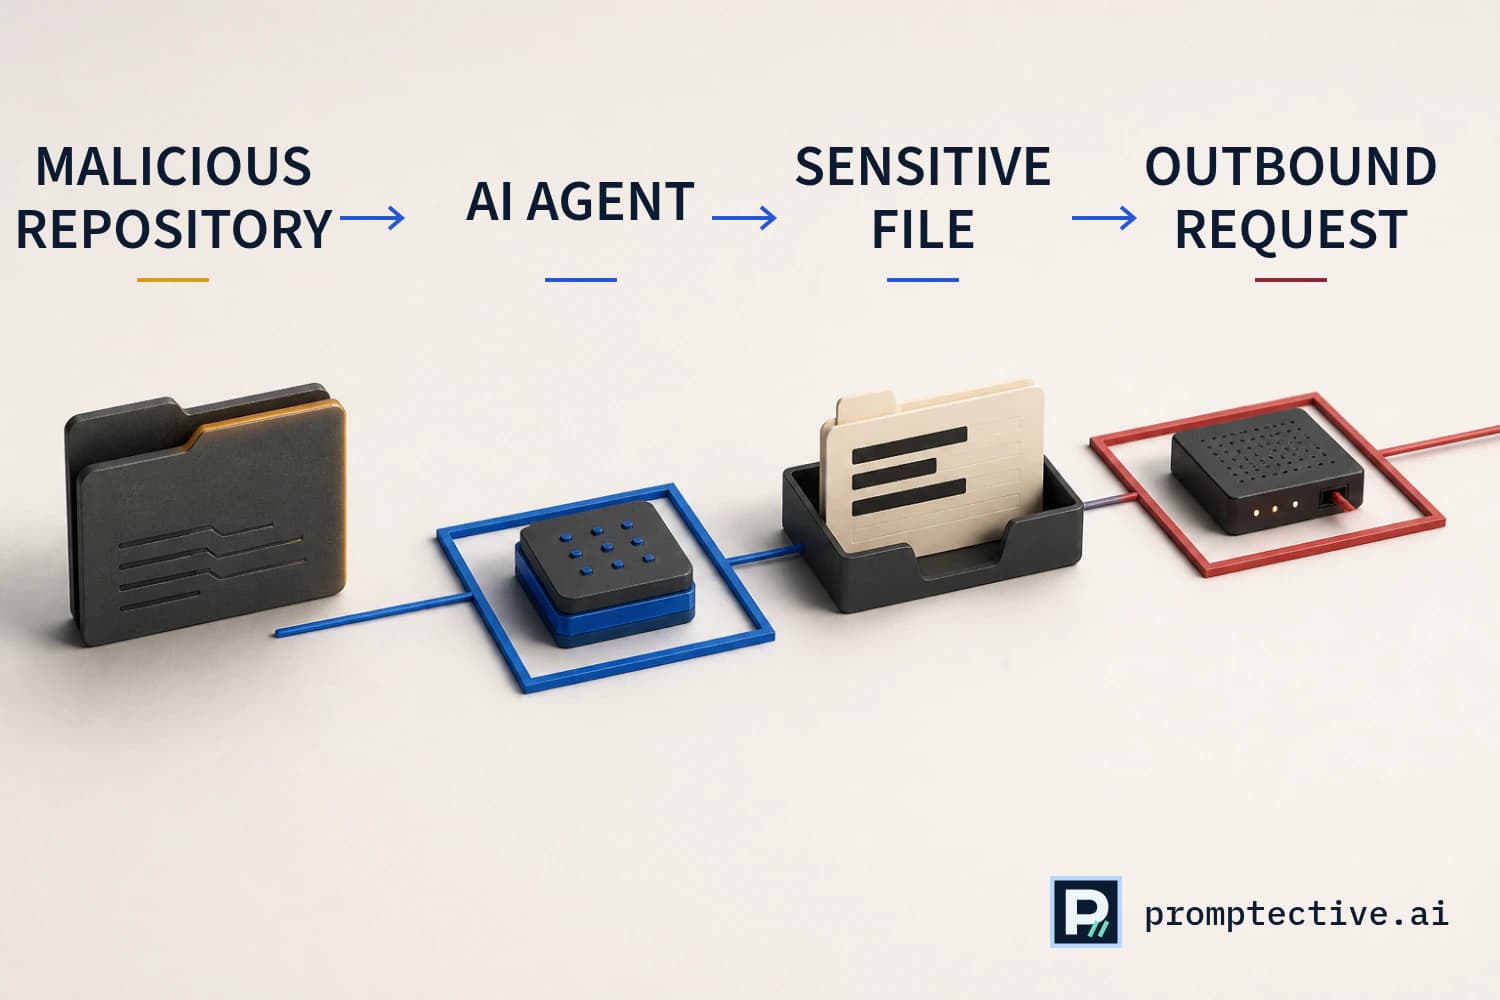
A Kiro prompt-injection flaw shows how repository content can steer an AI coding agent towards sensitive files, configuration changes and data exfiltration.

A failed hidden-message attempt in a Connecticut court shows what prompt injection protection must cover across enterprise document workflows.

What the 10 December 2026 APP 1 changes mean, which organisations are covered, how to map AI-supported decisions, and where Shadow AI discovery fits.
Practical reference

A practical workplace guide to prevent sensitive data reaching ChatGPT, Microsoft Copilot and GitHub Copilot using policy, DLP and tested controls.
Read guide

Compare five Nightfall alternatives by buyer fit, deployment and privacy. Find out when to keep Nightfall and what to test before switching.
Read guide

A practical guide to LLM security in production: control prompts, retrieval, outputs and tools; minimise sensitive evidence; test and respond.
Read guide

A practical framework for securing LLM applications at the boundary between trusted instructions, untrusted content, model output, and real-world actions.
Read guide

How attackers bypass LLM safety guardrails, the common techniques they use, and practical ways to defend AI applications.
Read guide

Learn how to reduce prompt injection, tool abuse, and MCP risks with practical controls for LLM agents and their connected systems.
Read guide

Review 15 illustrative prompt injection attack examples across direct, indirect and agent risks, with source-backed controls for reducing their impact.
Read guide

A practical guide to securing your AI applications against prompt injection, jailbreaks, and data exfiltration. Learn defence-in-depth strategies.
Read guide

Learn how prompt injection attacks work, see practical examples, and compare controls for protecting LLM applications in this 2026 guide.
Read guide
Website analytics are off.